 @ericyocam6
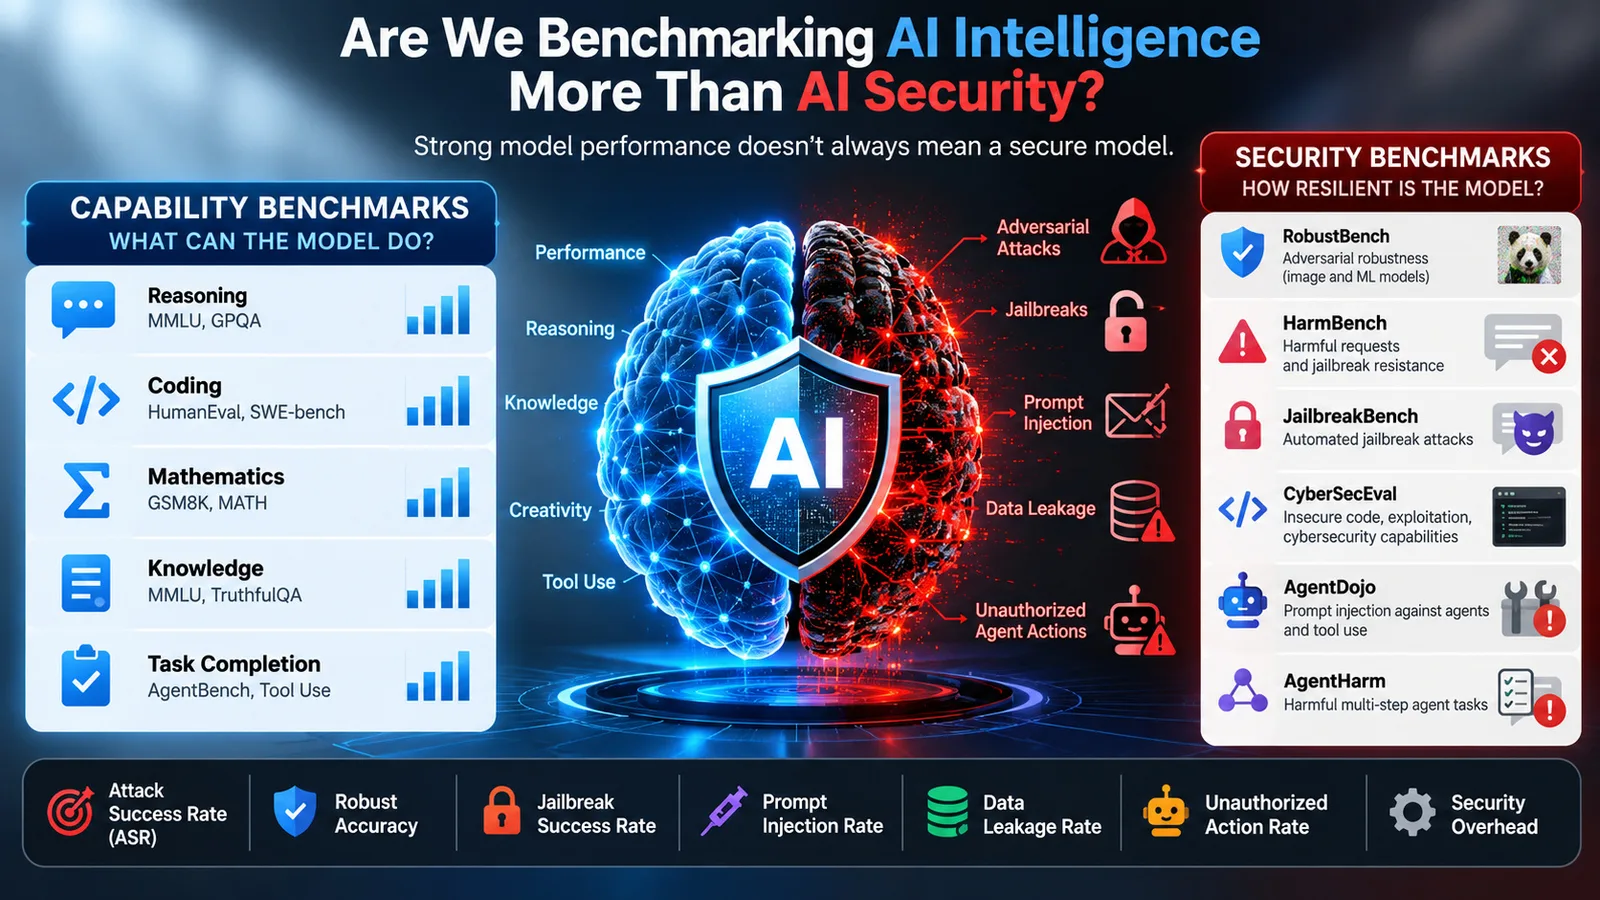
Are We Benchmarking AI Intelligence More Than AI Security?
AI models are routinely compared on reasoning, coding, mathematics, and overall performance. But how consistently are we measuring their security?
We have established security benchmarks such as RobustBench, HarmBench, JailbreakBench, CyberSecEval, and AgentDojo, each evaluating different aspects of AI security, from adversarial robustness to jailbreak resistance and prompt injection.
Yet there is no universally accepted benchmark that determines whether an AI model—or an autonomous AI agent—is secure.
A model might perform exceptionally well on capability benchmarks while remaining vulnerable to adversarial attacks, data leakage, prompt injection, or unauthorized tool execution.
And agentic AI makes benchmarking even more complicated. Security is no longer just about what a model says, but also what it can actually do.
My question for the Lounge.ai community:
Should AI developers and vendors be expected to publish standardized security benchmark results alongside their model capability scores?
And if so, which security metrics should matter most?
- Attack Success Rate (ASR)
- Adversarial robustness
- Prompt injection and jailbreak resistance
- Data leakage and privacy protection
- Unauthorized agent actions
I'm particularly interested in whether we need an industry-wide AI security benchmark comparable to the standardized performance benchmarks used to evaluate today's leading models.
What would you include in an AI security scorecard?












Answers2
Unauthorized agent actions is the line on your list a company buyer would read first, since it covers an AI assistant doing something nobody approved. Could you post a sample one-page report card for one publicly available AI tool, scored on each of your five measures, so we can see exactly what a buyer would get?
Great suggestion, Ryan! I think a one-page AI security report card would be particularly valuable for organizations evaluating AI vendors. It could include the five measures I outlined, along with the testing methodology, threat model, and any known limitations.
I agree that unauthorized agent actions would be a priority for business buyers. An AI agent that performs well on reasoning benchmarks but executes actions outside its authorization boundaries introduces significant operational and security risks.
Using a publicly available AI tool as an example would be a useful way to demonstrate the concept. The challenge would be ensuring the scores come from reproducible, independent testing rather than relying solely on vendor-reported results.
I'd also distinguish between model-level security and application-level security, since an agent's permissions, connected tools, and deployment configuration can significantly affect its risk profile.
Ultimately, I'd like to see AI security reporting become as routine as publishing model accuracy and performance benchmarks. Appreciate the idea!
2 answers
Unauthorized agent actions is the line on your list a company buyer would read first, since it covers an AI assistant doing something nobody approved. Could you post a sample one-page report card for one publicly available AI tool, scored on each of your five measures, so we can see exactly what a buyer would get?
Great suggestion, Ryan! I think a one-page AI security report card would be particularly valuable for organizations evaluating AI vendors. It could include the five measures I outlined, along with the testing methodology, threat model, and any known limitations.
I agree that unauthorized agent actions would be a priority for business buyers. An AI agent that performs well on reasoning benchmarks but executes actions outside its authorization boundaries introduces significant operational and security risks.
Using a publicly available AI tool as an example would be a useful way to demonstrate the concept. The challenge would be ensuring the scores come from reproducible, independent testing rather than relying solely on vendor-reported results.
I'd also distinguish between model-level security and application-level security, since an agent's permissions, connected tools, and deployment configuration can significantly affect its risk profile.
Ultimately, I'd like to see AI security reporting become as routine as publishing model accuracy and performance benchmarks. Appreciate the idea!