 @ericyocam7
Professor, California Polytechnic State University
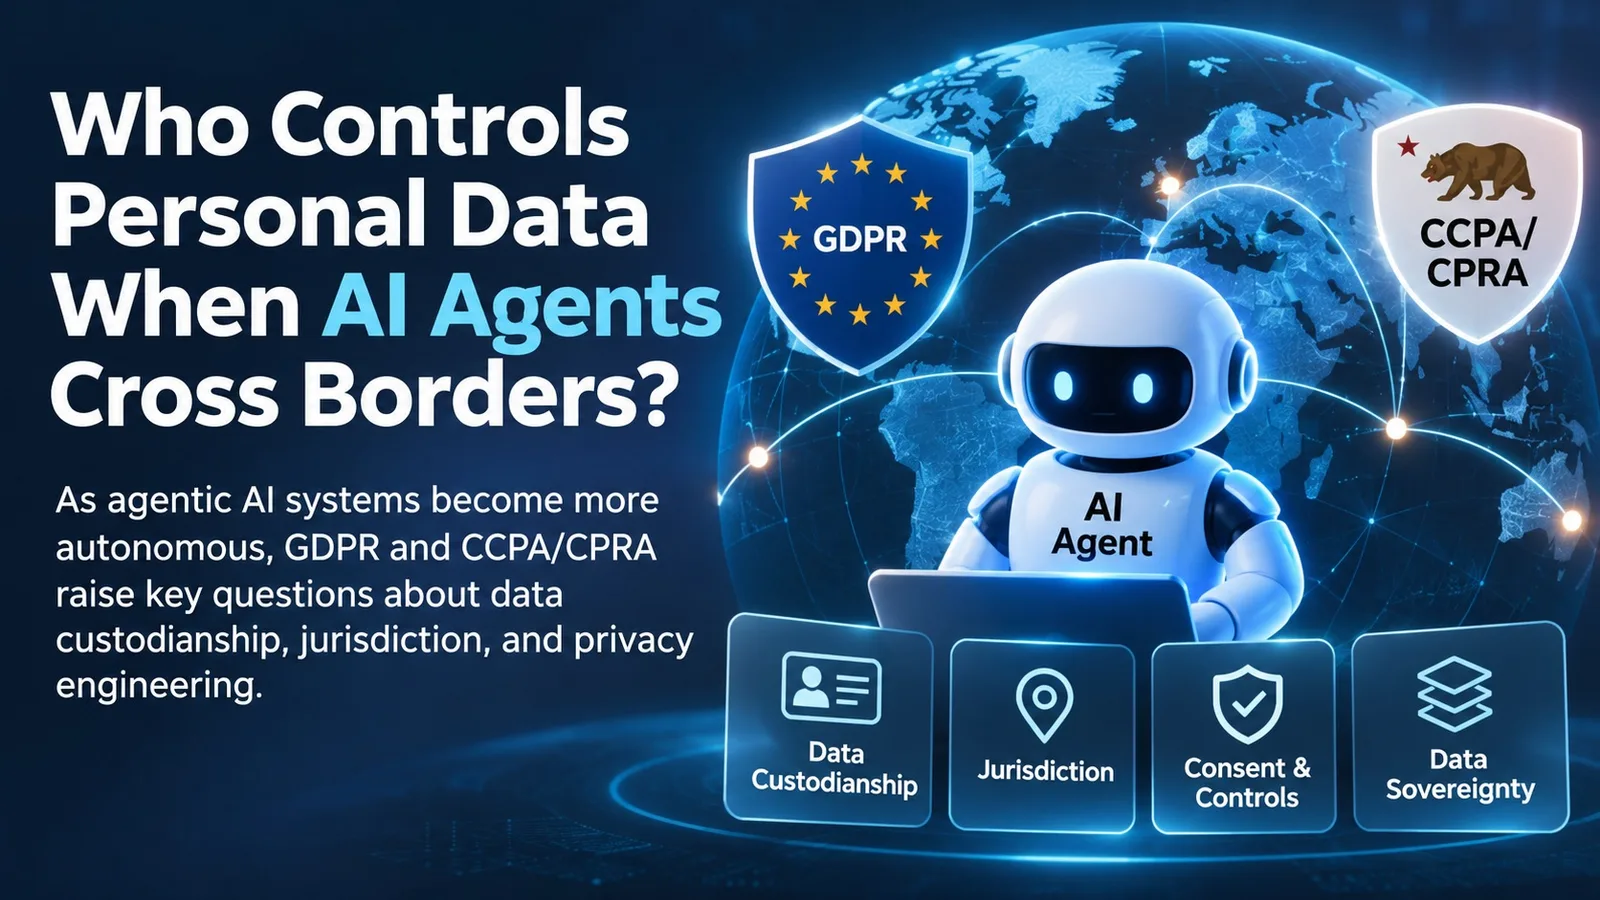
Who Controls Personal Data When AI Agents Cross Borders?
As agentic AI systems become more autonomous, an important privacy engineering question emerges: Who is responsible for personal data when AI agents access, process, and transfer information across different systems and countries?
Imagine a company in California using an AI agent that retrieves customer information, sends it to an external LLM, and delegates tasks to other agents operating in different jurisdictions.
Under GDPR and CCPA/CPRA, organizations remain responsible for meeting applicable privacy obligations. But autonomous agents introduce new challenges involving data custodianship, consent, jurisdiction, and accountability.
This raises questions about how privacy engineering should evolve.
- How do we enforce data sovereignty and jurisdictional restrictions?
- Who is accountable when agents share personal information across services?
- Should agents be allowed to transfer personal data without explicit authorization?
- Can data provenance and independent policy enforcement provide adequate safeguards?
My question for the Lounge.ai community:…