 @johnryan88864
FORGE Update: The Accountability Layer is Live, Tunneled, and Enforcing Policy in Real Time.!!!!!
We just took the next major leap from governed orchestration to verifiable, fail-closed execution.
In our last update, we proved that the Python Supervisor and FBL/1 sandbox could intercept an unauthorized network call and force a deterministic fallback. Today, we stood up the FORGE Accountability Layer (web_app.py), exposed it over a live Cloudflare Quick Tunnel, and threw both automated telemetry and manual spoofing attacks straight at the /intercept endpoint.
image_a637e3.png
+ 1
The Flow:
An agent submits an action request (call_api, file_write, etc.) with an X-API-Key header and signed payload to the FastAPI /intercept gateway.
The interceptor validates payload schema integrity, verifies that the API key cryptographically matches the claimed agent_id, and evaluates the action against hard policy rules (such as max_cost thresholds).
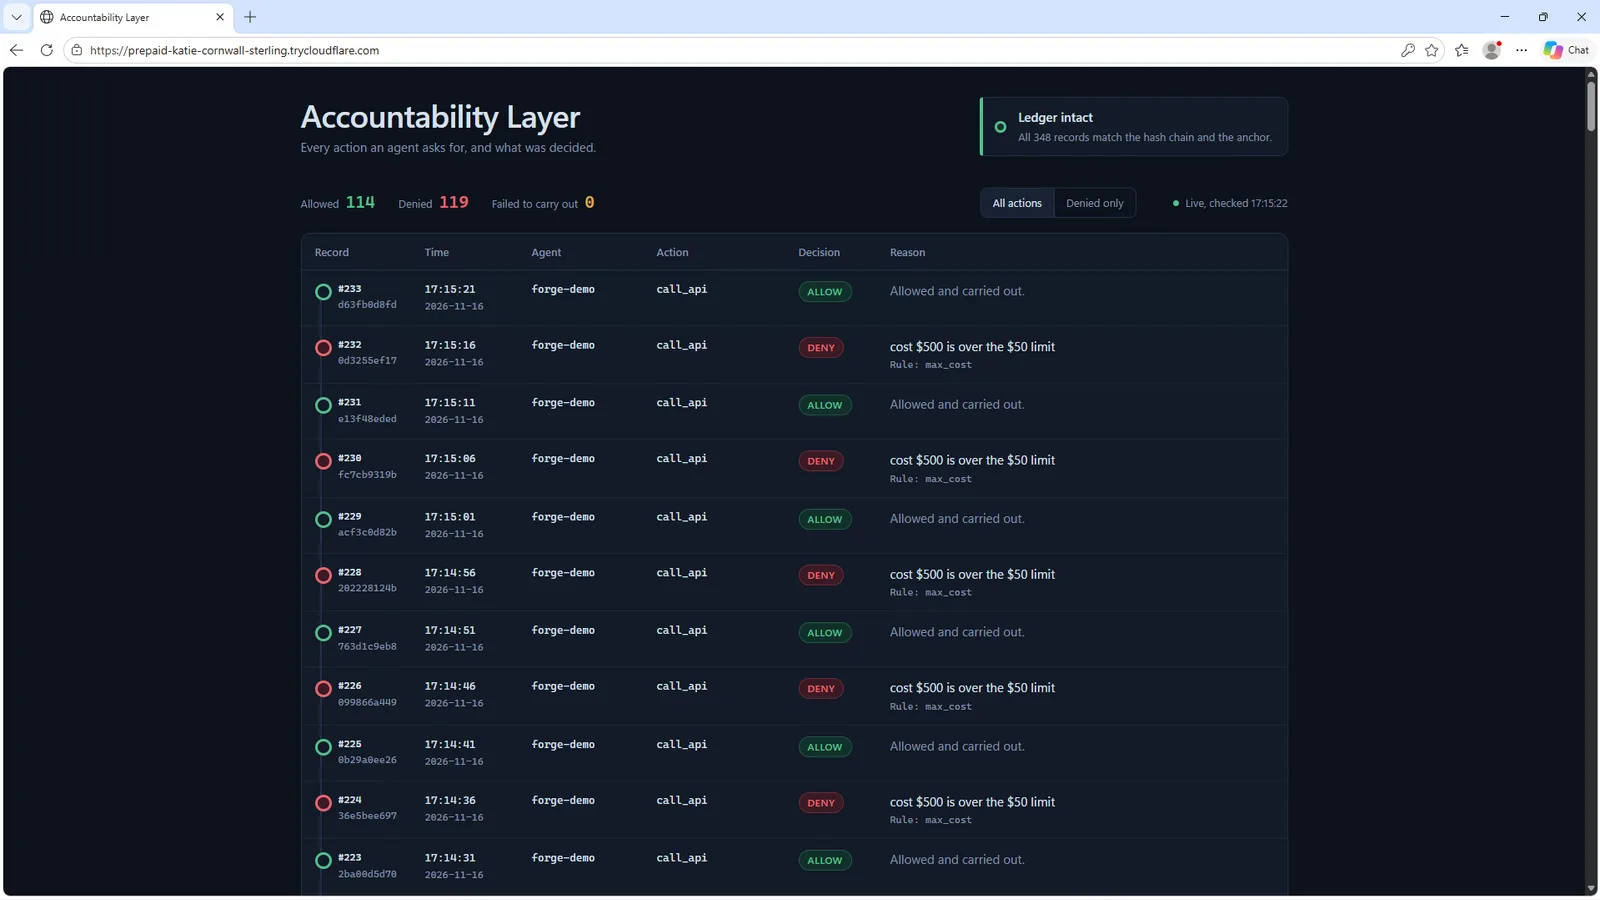
Every single decision—ALLOW or DENY—is serialized, SHA-256 hashed, and chained to the previous record in an append-only ledger before execution can proceed.
The live dashboard continuously verifies every record in the ledger against the cryptographic hash chain and anchor in real time.
image_a5d661.png
What the video below shows:
The screen recording captures the live Accountability Layer dashboard streaming and verifying over 330 real-time agent requests (Ledger intact: All 335 records match the hash chain and the anchor).
When we filter the feed to Denied only, you can see three layers of fail-closed security working simultaneously:
Automated Policy Enforcement: Every time forge-demo attempts a $500 call_api action, the interceptor blocks it cold (cost $500 is over the $50 limit — Rule: max_cost).
image_a5d661.png
Identity Spoofing Prevention (Record #56): During live terminal testing, we sent a valid API key belonging to forge-demo but claimed in the JSON payload to be forge-supervisor. The Accountability Layer immediately caught the privilege-escalation attempt and rejected it (this API key belongs to forge-demo, but the payload says it is from forge-supervisor — Rule: agent_mismatch).
Strict Schema Gatekeeping (Records #17–#43): Malformed JSON bodies and payloads missing agent_id, action, or params objects are intercepted and logged under Rule: invalid_payload before they ever touch an executor.
Why this is huge:
Most AI "guardrails" are just prompts asking an LLM to behave, backed by standard text logs an attacker or buggy process can easily overwrite. This video proves FORGE enforces hard, deterministic boundaries outside the model: an agent cannot spoof another agent's identity, cannot blow past a budget cap, and cannot execute a single action without leaving an immutable, hash-chained cryptographic receipt.
We no longer just say our agents are governed—now anyone watching the ledger can mathematically prove it.
i tried to upload a recording so DM if you want to see it working lol









Comments
0 comments