 @raresney1
Take a look
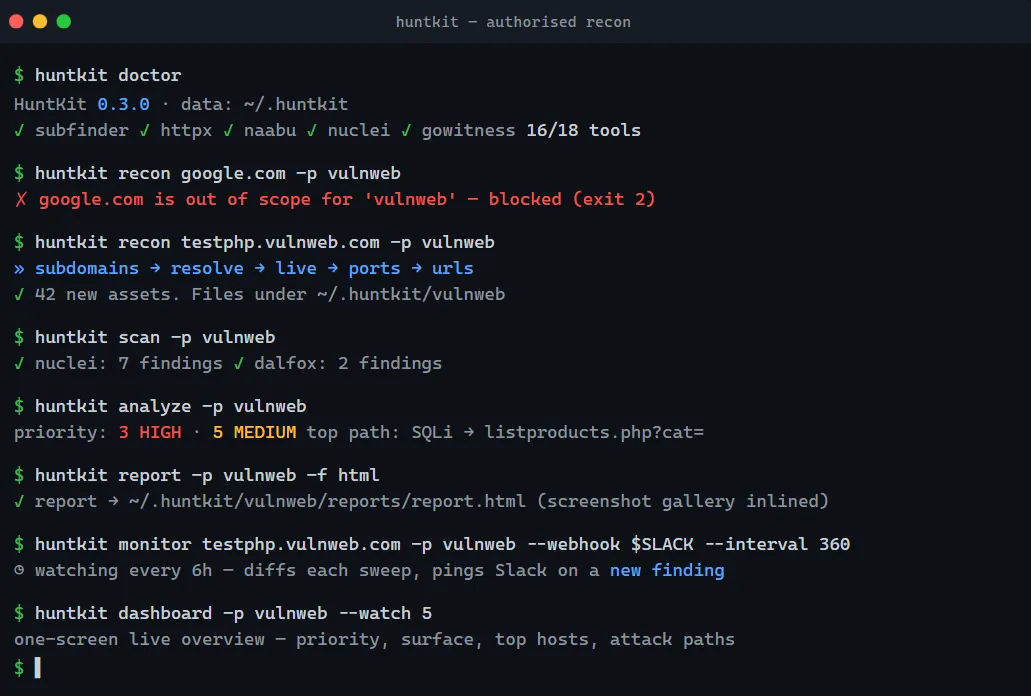
I've been working on HuntKit, an open-source, local-first framework designed to streamline and improve bug bounty reconnaissance and security testing.
The idea behind HuntKit is simple: instead of manually managing multiple security tools, workflows, outputs, and reports, bring everything together into one structured environment.
What makes HuntKit different?
- Automated, parallel and resumable reconnaissance pipelines.
- Integration with tools like Subfinder, httpx, Naabu, Nuclei, FFUF, Dalfox and more.
- Scope enforcement to prevent testing unauthorized assets.
- An intelligence engine that scores attack surfaces and prioritizes potential attack paths.
- Built-in vulnerability research playbooks covering 9 bug classes.
- Automated reporting in Markdown, HTML, JSON and PDF.
- Optional AI-assisted analysis using local Ollama models or cloud providers with explicit approval.
- Continuous monitoring, result comparison and notifications for new findings.
- A local-first architecture: engagement data stays on your machine by default.
HuntKit is built for security researchers and bug bounty hunters who want a more organized, efficient and reproducible testing workflow.
Tech stack: Python, CLI tooling, external security tools, AI integrations and Docker.
GitHub: github.com/Raresney/HuntKit
PyPI: pypi.org/project/huntkit/
I'm currently looking to connect with people working in cybersecurity, offensive security, AI-assisted security research and automation.
I'd especially appreciate feedback on the architecture, feature set and potential directions for future development.
Always intended for authorized security testing only.








Comments
0 comments